Security reviews for your PRs
Greptile pairs static scanning with an AI security agent to catch vulnerabilities in every pull request.
no credit card required • 14-day free trial
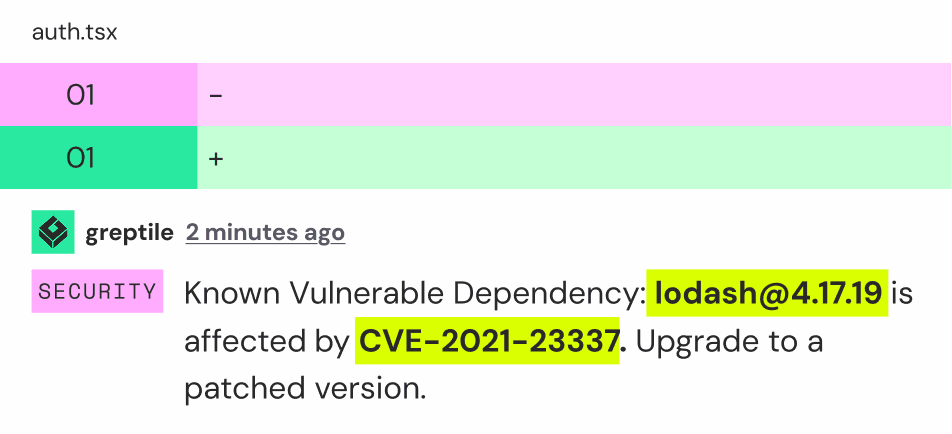
How Greptile security review works
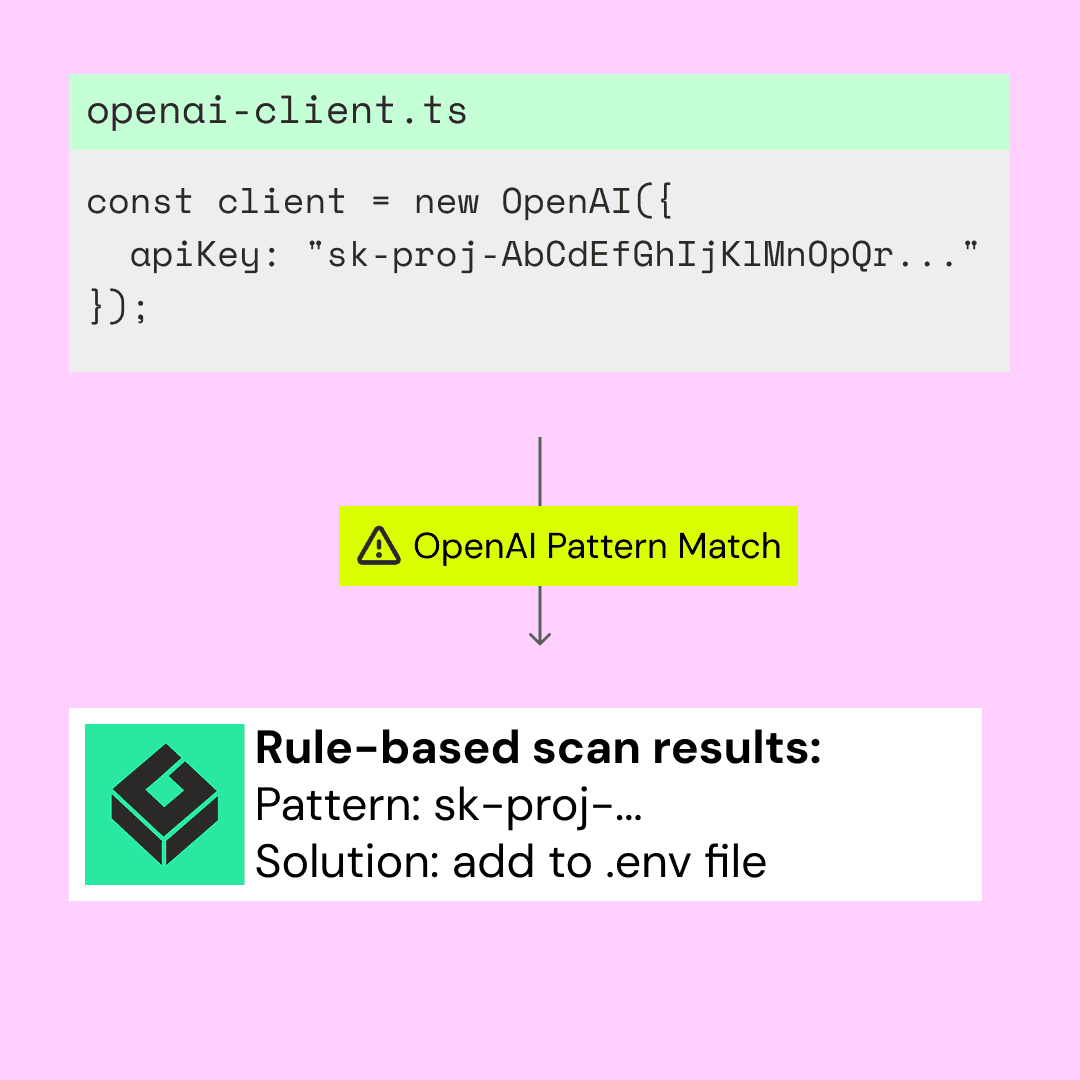
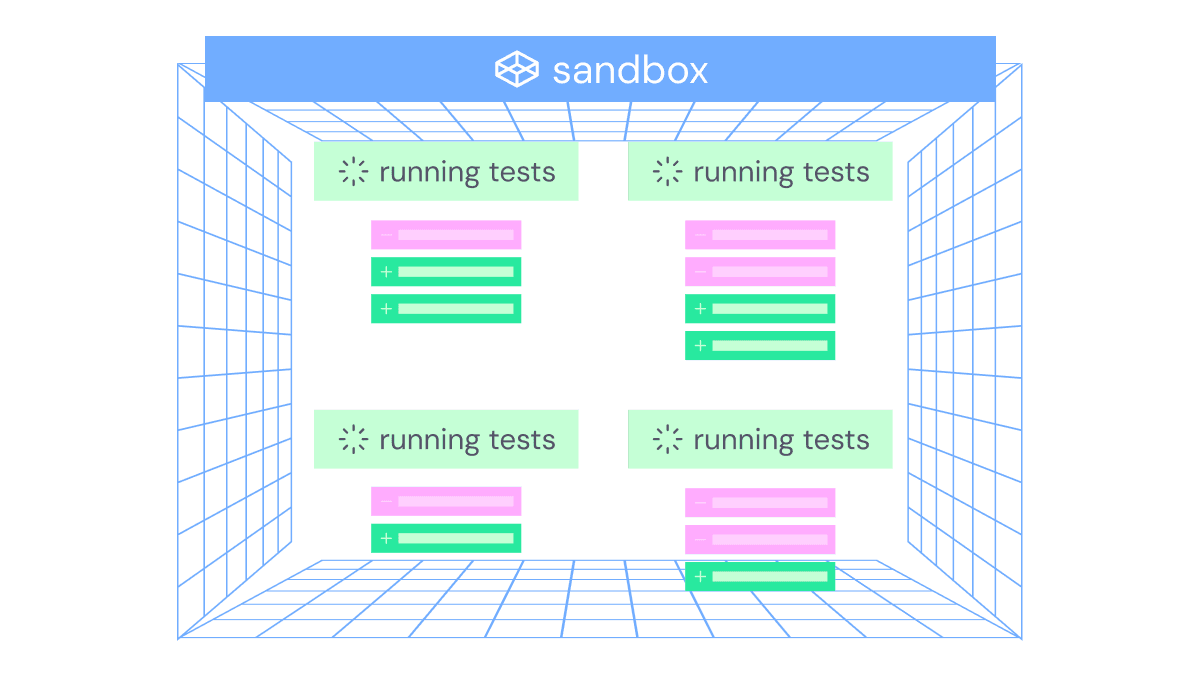
Opengrep rule-based scanning
Pattern-matching rules that catch dangerous code constructs deterministically.
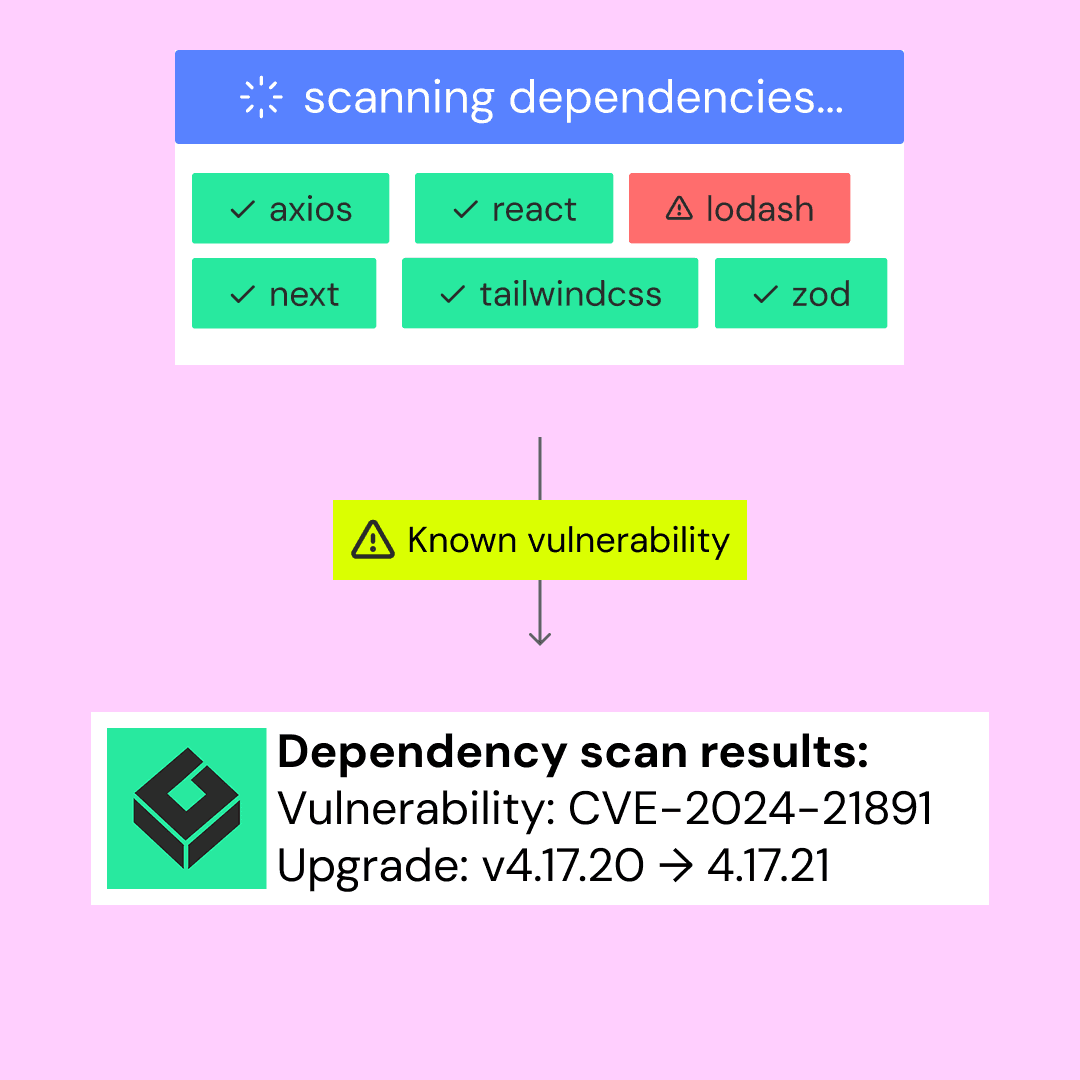
SCA to identify CVEs
Software composition analysis that checks your dependencies against known vulnerability databases.
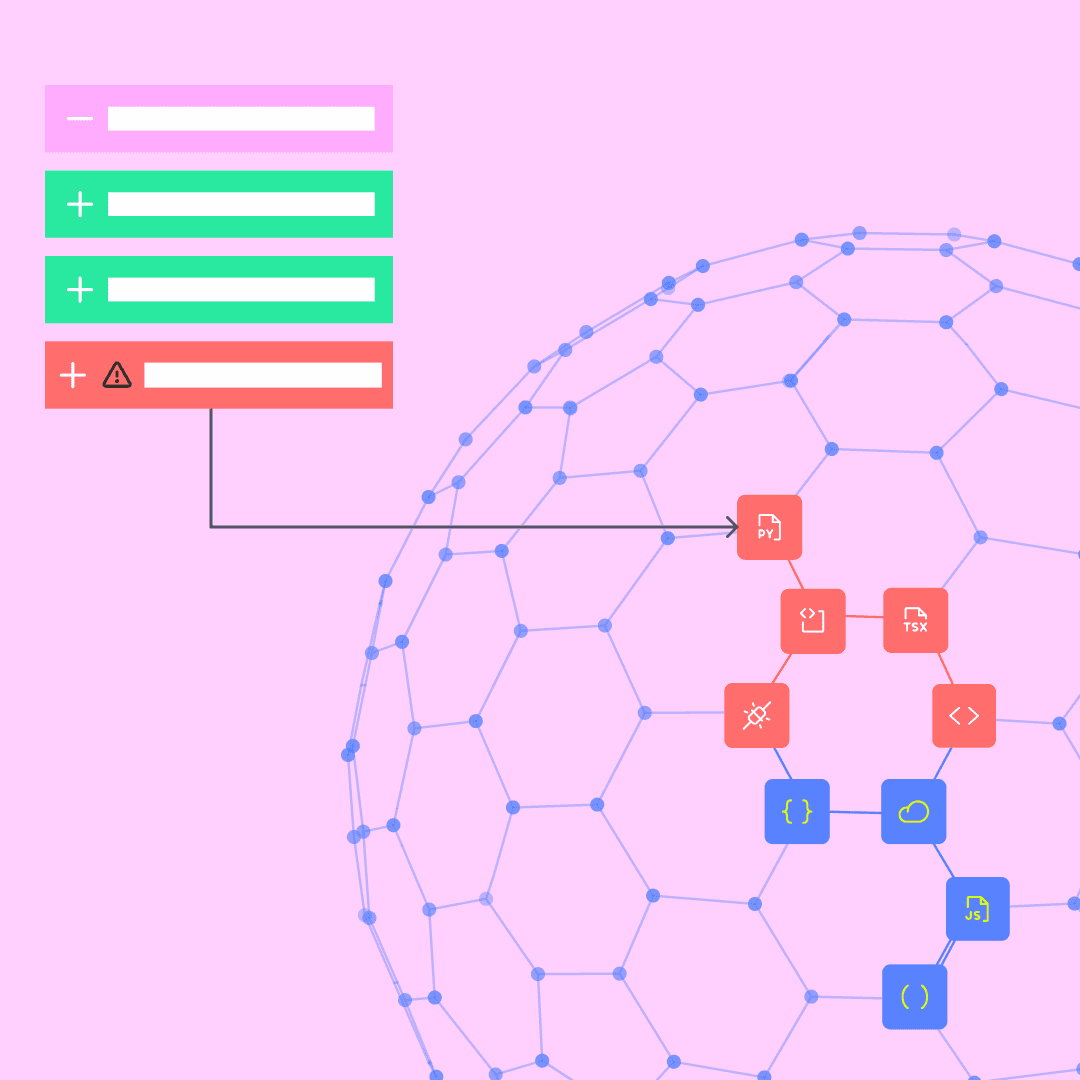
AI to detect chained exploits
Non-deterministic analysis that understands context and catches issues static tools can't.
Examples
Security findings from recent pull requests.
Authorization bypass
A stale DNS challenge could mark a domain verified after its ownership state changed.
Filesystem and PATH attack
A PATH fallback could run an attacker-controlled gh binary during a PR check.
Denial of service
A malformed peer-presence message could disconnect collaboration and halt document sync.
Security-gate bypass
An allowlisted command could satisfy the security gate before review verification ran.
Explore other features at Greptile
Find out more about how teams are using Greptile
Find security vulnerabilities before they ship